Uptime, every 30 seconds
Checks from outside as often as every 30 seconds. Each one times DNS, the connection, the TLS handshake and the first byte, so "slow" comes with its cause.
Everything Servertorch does, in the console today. Each item says which plan it starts on and, where it matters, what has to be installed for it to work.
What Servertorch can see depends on how much you connect, not on what you pay. None of it needs SSH or root.
Add an address and checks start within a minute, the way a visitor sees your site.
No server load, traffic or attack data. None of that is visible from outside.
One PHP file for shared hosting, or a package for Node.js, Python, .NET, Java, Go or Ruby, or an edge guard for static sites.
Everything the guard does, plus what only makes sense inside WordPress.
Connect the repository the site is deployed from. Nothing is installed and nothing in it runs.
Know the moment something breaks, which layer broke and what to do. From outside with nothing installed, and from inside with the guard.
Checks from outside as often as every 30 seconds. Each one times DNS, the connection, the TLS handshake and the first byte, so "slow" comes with its cause.
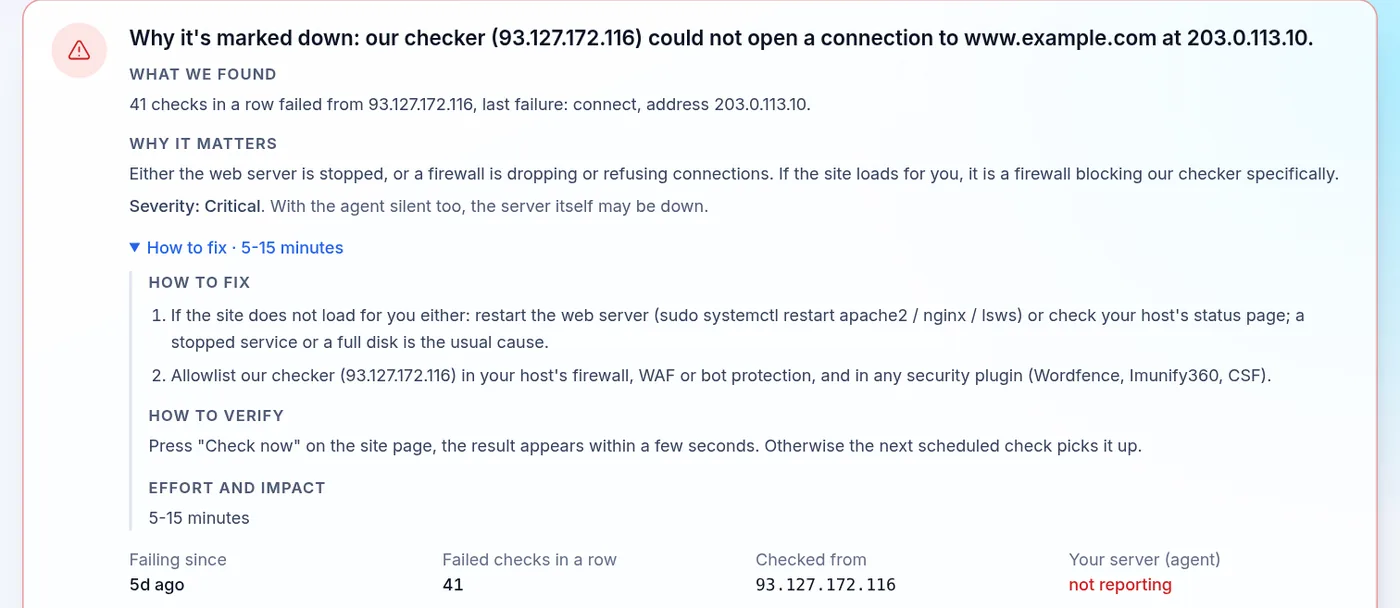
When a check fails the incident says which layer failed, the exact error, how serious it is and the steps to fix it. Failures collapse into one incident with a start, an end and a timeline.
Expiry, chain and hostname checked all the time, so you hear about a certificate weeks before a visitor does. DNS records are kept with the date each one changed.
Each missing header graded, with the exact line for Apache, Nginx or your CDN. Spam and malware lists checked, Safe Browsing included.
Live visitors, hits, top pages, 4xx and 5xx errors and response times, from your server's own records. Real visitor IPs behind Cloudflare. People separated from bots.
Works out which CDN you are behind and whether your origin server still answers directly, which quietly makes the CDN pointless.
Email, Slack, Microsoft Teams, Telegram, signed webhooks and browser push, per site and per severity. Repeat alerts are throttled, so one outage is one message.
A page your customers can check during an outage, so your phone rings less.
A firewall that runs inside your site, file checks that catch what got in, and rules for known holes until you patch them.
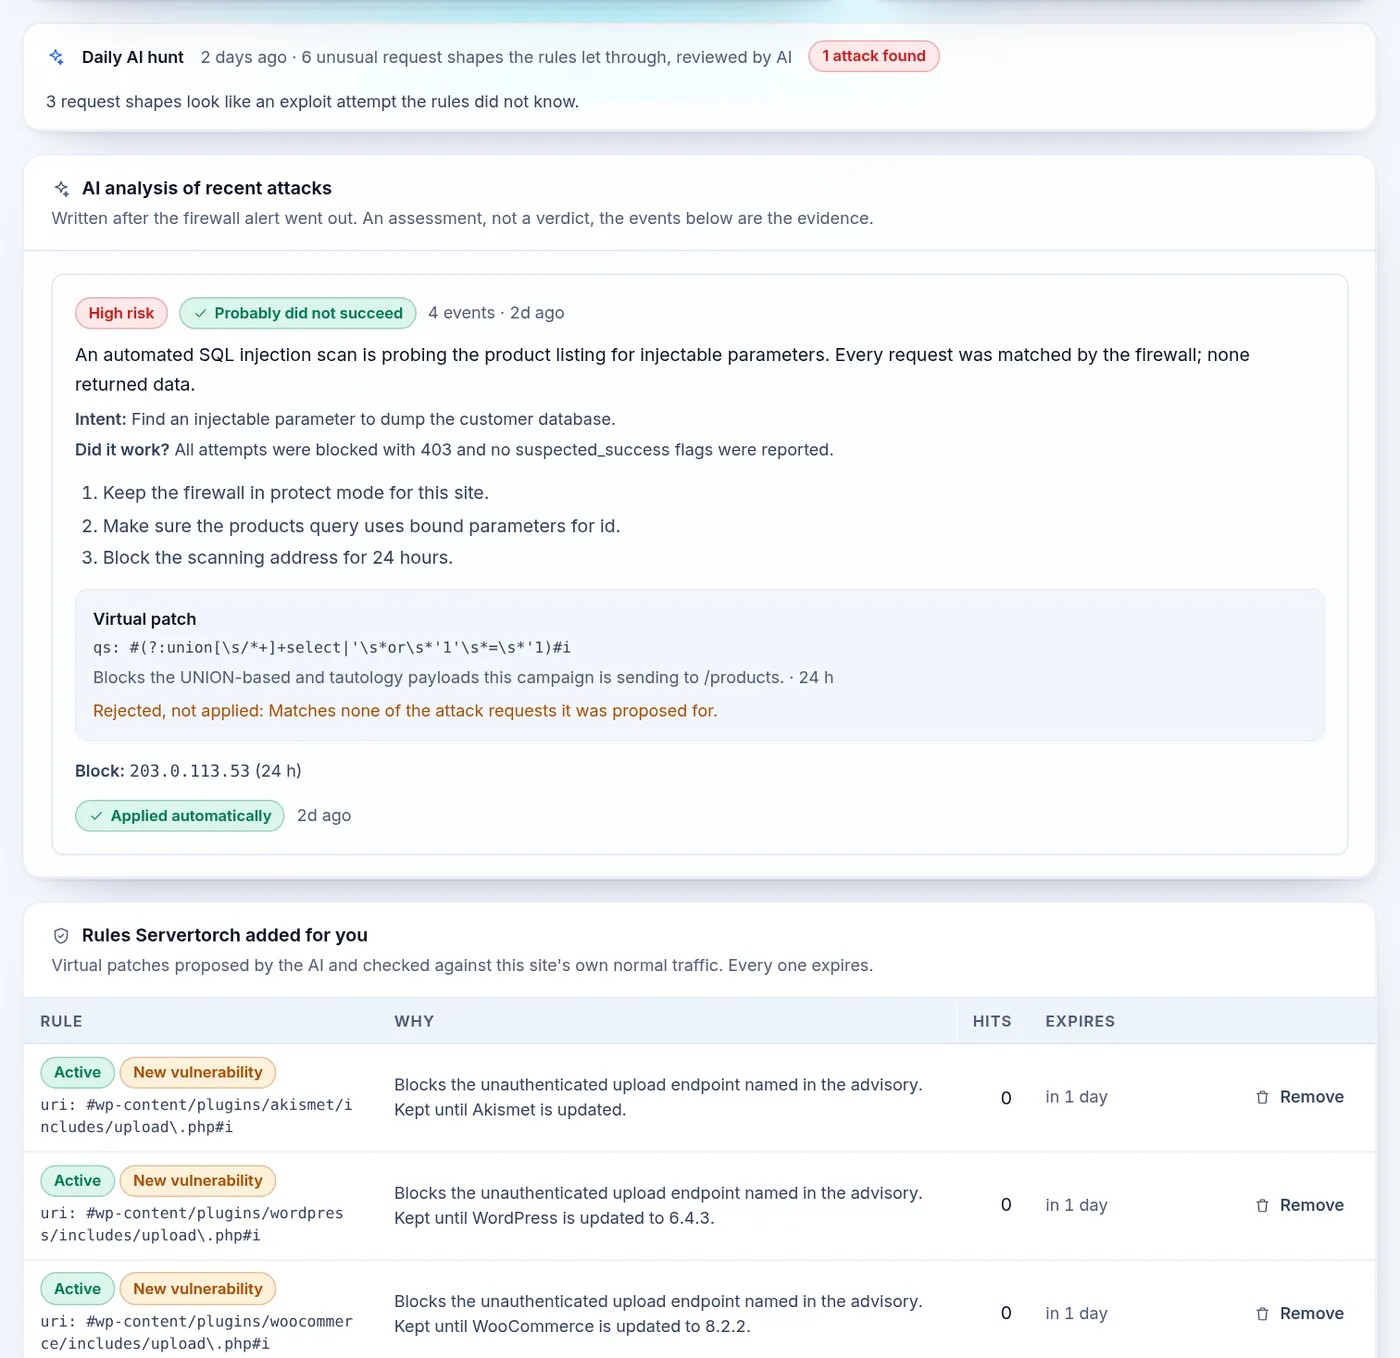
Blocks SQL injection, XSS, path traversal, bad bots and brute force inside your application. Every block comes with the attacker's own request.
Block an address or range from the evidence, set rate limits, and have the firewall refuse attacks rather than only record them.
A hash of every file, compared on a schedule. Changed and added files are flagged with the matched line, so a web shell in uploads/ or a spam injection shows up the same day.
Every night WordPress core, plugins and themes are checked against a vulnerability database. A vulnerable component opens an incident and gets a temporary blocking rule for the published exploit until you update it.
A rule learned from an attack on one Servertorch site is offered to every other site on the same platform. Each site tests it against its own normal traffic first.
PHP settings that should be off, files writable when they should not be, and for WordPress, database hardening checks.
AI explains, sorts out the noise and writes narrow rules. Blocking and alerting never wait for it, and never depend on it.
A new attack pattern is read by AI: what it was after, whether it worked, what to do on your stack. Usually within a minute of the alert. Repeats of a pattern it has read are linked for free.
For a new attack the AI writes a narrow rule, tests it against your site's own normal traffic, and applies it automatically or on one click. Every rule expires on its own.
Once a day the unusual traffic that no rule flagged is reviewed by AI to find attacks the rules did not know. What it finds goes through the same alert and patch path.
AI reads your public pages and every finding we already have (headers, TLS, readiness, integrity, vulnerable components) and turns them into one list of what to fix, each with evidence.
Every code finding is double-checked by AI: confirmed with a plain why and fix, or set aside as a false positive. The riskiest changed files get a review of their own. Only changed files are re-sent.
Ask about your own sites in plain words. "Why was the shop slow on Tuesday?" Nekoba sees your account and answers from your data.
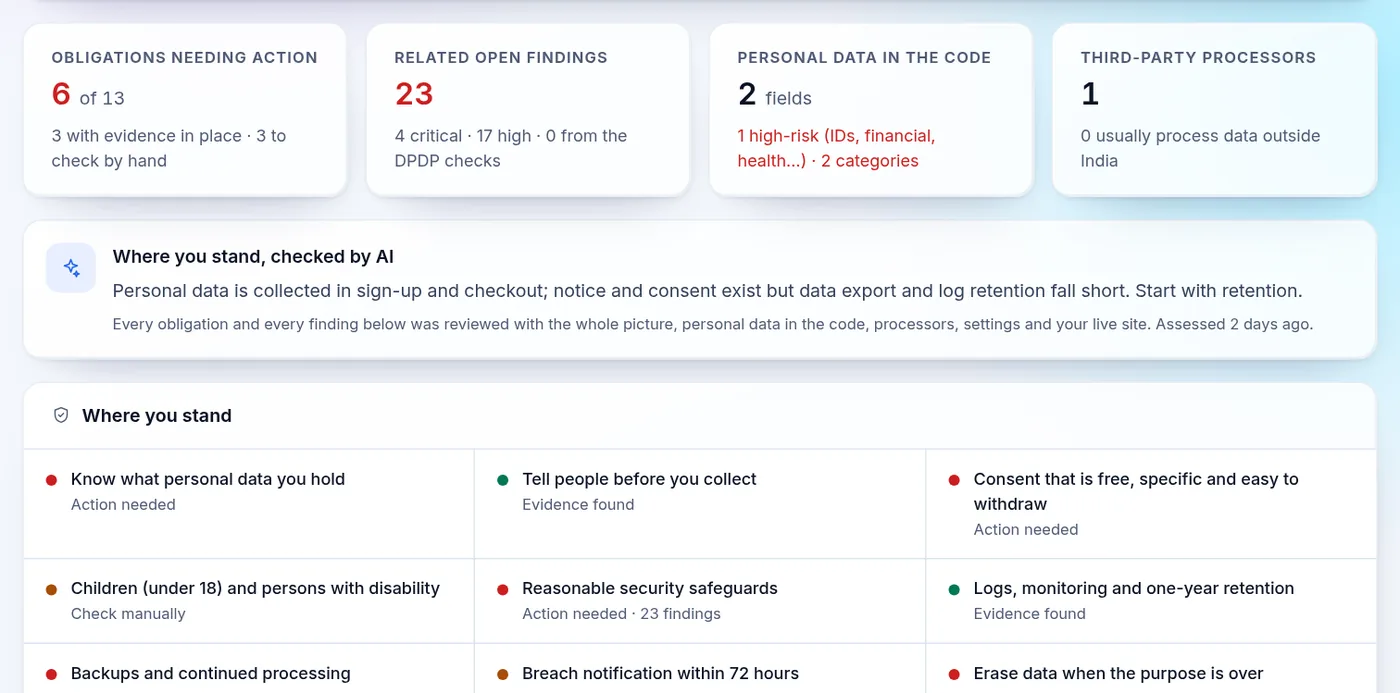
India's DPDP Act 2023 and the DPDP Rules 2025, checked on your pages and in your code, with a report you can hand over.
Per site and per repository: which obligations are met, need action or do not apply, from what our scanners saw. With an AI assessment for each obligation.
Which trackers load before anyone consents, whether a banner records a decision or only announces one, and forms that collect personal data without consent.
Aadhaar, PAN, phone, health and bank fields: where they are stored, logged and sent. Mapped to the Rules, with the fix.
The report prints cleanly, with what was checked, what was found and what still needs a check by hand.
Readiness is checked again weekly and you get an email only when something changed. Usually that is a new tag somebody added.
Run the outside check on any site at /check in about fifteen seconds. It never uses AI.
The parts that matter once more than one person, or more than one client, is involved.
Owner, admin, member and viewer roles. Passkeys or an authenticator app for two-factor sign-in. An audit log of who changed what.
For agencies: each client is its own company with its own sites, people and alerts. One client never sees another.
Uptime, incidents and security for any period, as a page, a download or a scheduled email. With white label they carry your logo and colours.
Bearer-token access to the same JSON API the console uses, and signed webhooks for your own tools.
Proper tax invoices with CGST and SGST within the state, IGST across it, zero-rated for exports. TDS is recorded against the invoice.
Pay online through Razorpay, or by bank transfer. Pay a period early if it suits your books; there is a grace period if a payment runs late.
Better to know before a demo than after a month.
The free check runs on your own domain in about fifteen seconds. A plan puts all of it on your sites today, or book a demo and we set it up with you.
No free trial. Monthly, with a proper GST invoice. Demo replies within one working day.
No tracking cookies here
We only use the cookies needed to sign you in and keep forms safe. No analytics, no ads, nothing to accept.