Know when your site breaks, why, and what to do.
Servertorch watches your websites from outside and from inside, blocks attacks in the site itself, and explains every alert in plain words. It also checks your pages and code for gaps under India's DPDP Act. Built in Mohali for Indian businesses and the agencies that run their sites.
- No SSH or root needed
- Start today, or book a demo first
- GST invoice, pay by UPI or card
The console, replaying an example incident. Example data.
Most website problems are found by a customer first.
A shop that will not load, a login page that is quietly being brute-forced, a plugin with a published hole. By the time someone phones you about it, it has usually been going on for a while.
The site was down and nobody knew.
An expired certificate, a DNS record someone changed, a full disk on the server. Each one looks the same to a visitor: the site does not open.
Something changed and nobody saw it.
A web shell in uploads/, spam links in the footer, a plugin nobody has updated since the person who installed it left.
DPDP applies from 13 May 2027.
Trackers that load before consent, no named contact for data questions, Aadhaar numbers in plain text. Penalties go up to ₹250 crore.
Start from the outside. Go deeper when you want to.
Add a site and checks begin within a minute, with nothing installed. Each step after that is optional, takes a few minutes, and never needs SSH or root access to your server.
From the outside
Add an address and checks start within a minute, the way a visitor sees your site.
- Uptime as often as every 30 seconds, with DNS, connect, TLS and first byte timed
- Certificate expiry and chain, DNS changes, security headers, blocklists
- Which CDN you are behind, and whether the origin answers directly
- DPDP readiness of your public pages
A guard in your stack
One PHP file for shared hosting, or a package for Node.js, Python, .NET, Java, Go or Ruby, or an edge guard for static sites.
- Every request: path, status, timing and the real visitor IP behind Cloudflare
- Web firewall in the site: SQL injection, XSS, traversal, bad bots, brute force
- File integrity: changed and added files, web shells, spam injections
- Server load, memory and disk where the host allows it
WordPress plugin
Everything the guard does, plus what only makes sense inside WordPress.
- Core, plugin and theme inventory with versions
- Nightly check against a vulnerability database, with a temporary blocking rule until you update
- Hardening checks and login protection
Your source code
Connect the repository the site is deployed from. Nothing is installed and nothing in it runs.
- Secrets, risky code and vulnerable packages, with one fix command per manifest
- Personal data in the code, mapped to the DPDP Rules
- Every finding double-checked by AI, false positives set aside
The guard and the plugin are small, readable and fail open: if they cannot reach us, your site carries on as normal.
Four jobs, one console.
Most teams use three or four tools for this and still find out from a customer. Servertorch puts the monitoring, the firewall, the explanation and the compliance view in one place.
Monitor
Know the moment something breaks, and which layer broke.
- Uptime checks as often as every 30 seconds
- DNS, connect, TLS and first byte timed on every check
- Certificates, DNS changes, headers, blocklists
- Live visitors, top pages, 4xx and 5xx errors
- Alerts by email, Slack, Teams, Telegram, webhook, push
Protect
A firewall that runs inside your site, not in front of it.
- Blocks SQL injection, XSS, traversal, bad bots, brute force
- File integrity: web shells and spam injections caught
- Known-vulnerable WordPress plugins blocked until you update
- One site's attack protects every other site on the platform
Fix with AI
Plain words for every finding, and rules written for new attacks.
- Every new attack read, explained and given a narrow virtual patch
- A daily hunt through traffic no rule flagged
- AI site review: one list of what to fix, with evidence
- Code findings double-checked, false positives set aside
Comply
Get ready for India's DPDP Act before May 2027.
- Readiness report per site and per repository
- Trackers before consent, notices, forms, retention
- Personal data in your code, mapped to the Rules
- Printable PDF for your board, auditor or client
What it looks like when something happens.
Screenshots from the product, with demo data. No mock-ups.
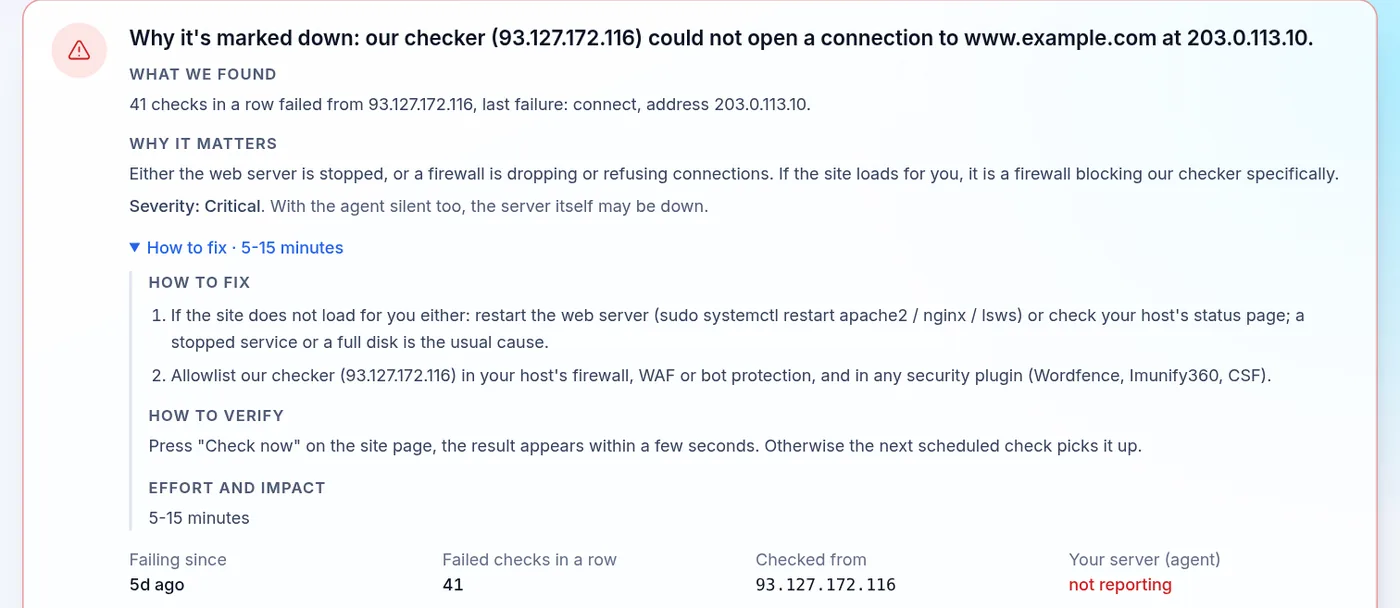
When a site goes down, it tells you why.
Every check times DNS, the connection, the TLS handshake and the first byte separately. When one fails, the incident says which layer, what the error was, how serious it is and the steps to fix it, in words you can forward to your hosting company.
- Repeat alerts are grouped, so one outage is one message
- Public status page for your customers
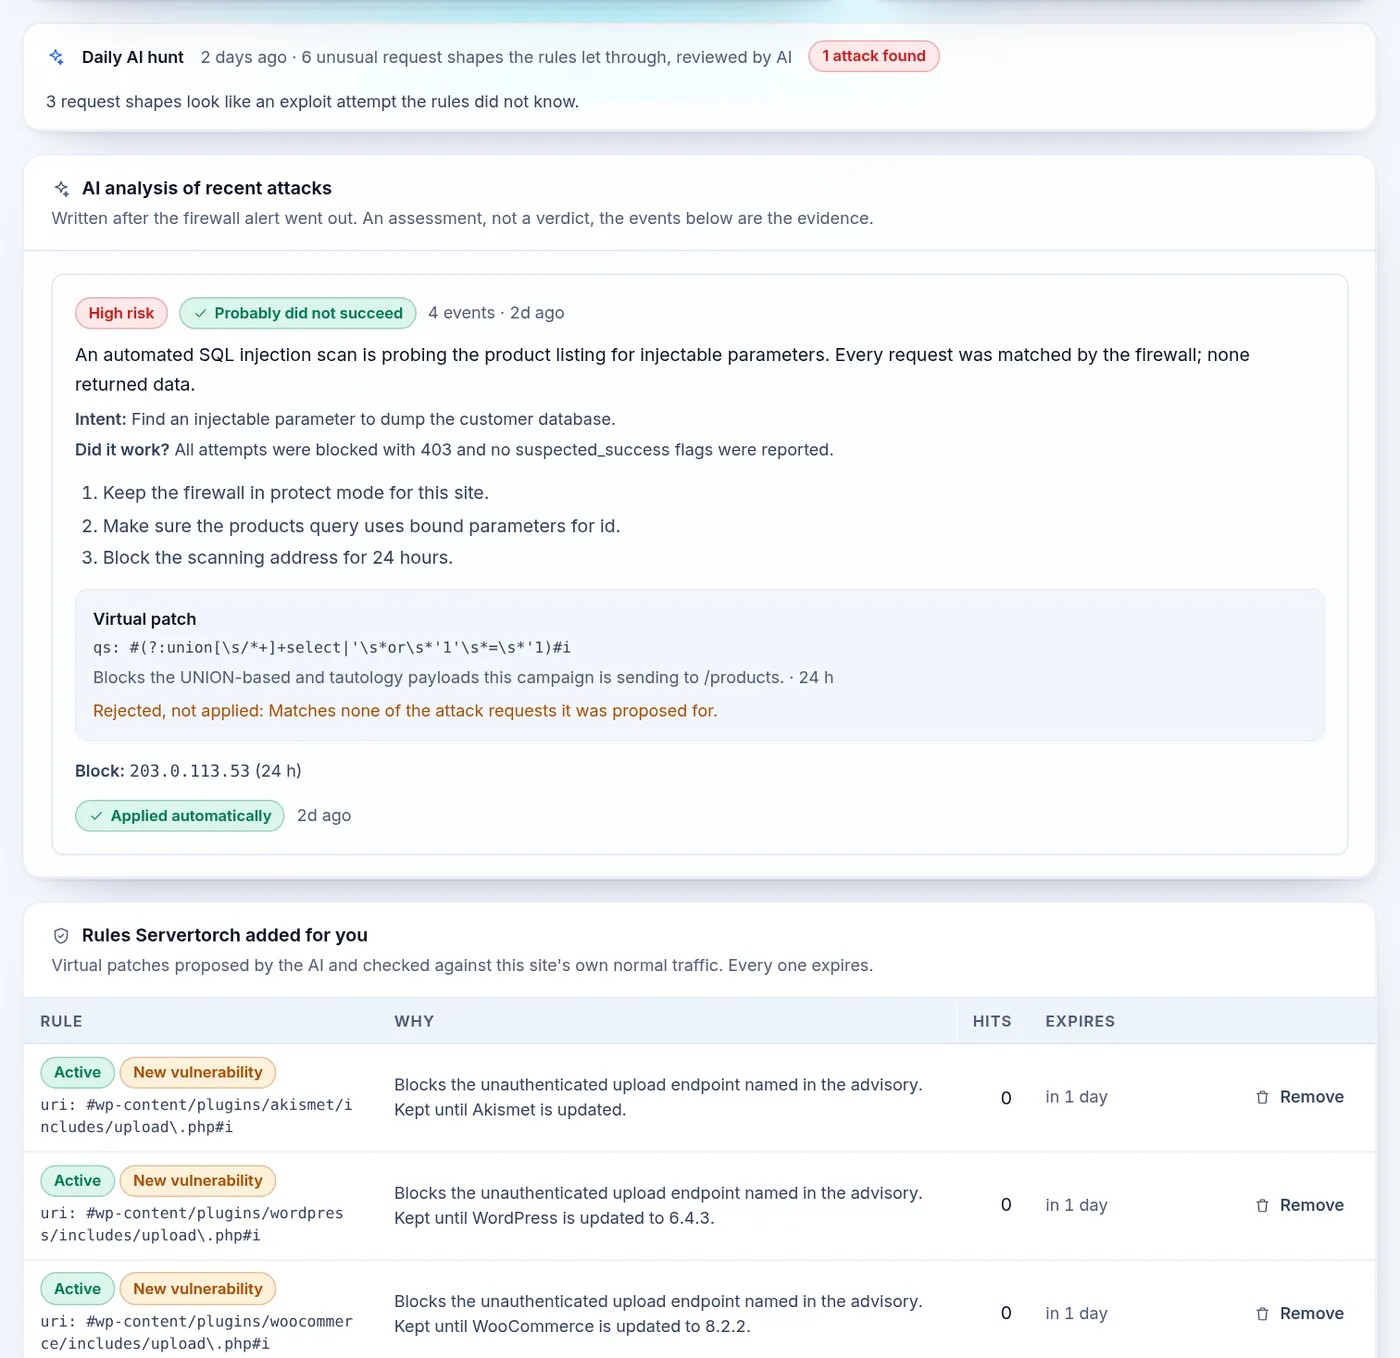
A new attack gets a rule of its own.
The firewall blocks what it knows in the request itself. When an attack pattern is new, our AI reads it, explains what it was after and whether it worked, and writes a narrow virtual patch. The patch is tested against your site's own normal traffic before it goes live, and it expires on its own.
- Applied automatically, or with one click, your choice
- Shared with every other Servertorch site on the same platform
- Once a day, AI hunts through traffic that no rule flagged
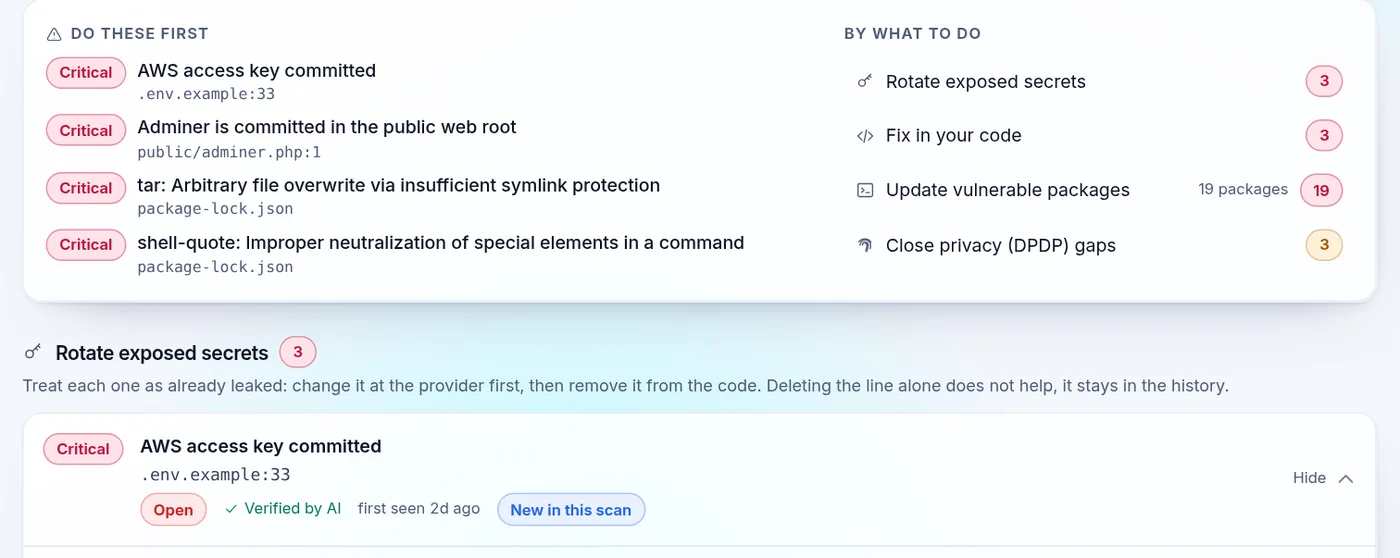
Code findings you can act on today.
Connect the repository and get secrets, risky code and vulnerable packages, grouped by what to do about them. Each finding is double-checked by AI before it reaches you, so the list is short and true.
- One fix command per package manifest
- Only changed files are reviewed again
A DPDP report you can hand to your board.
Each of the obligations in the DPDP Act and Rules is marked as needing action, evidence found, check by hand, or not applicable, from what our scanners saw on your site and in your code. AI writes a short assessment for each one. Download it as a PDF.
What the DPDP check covers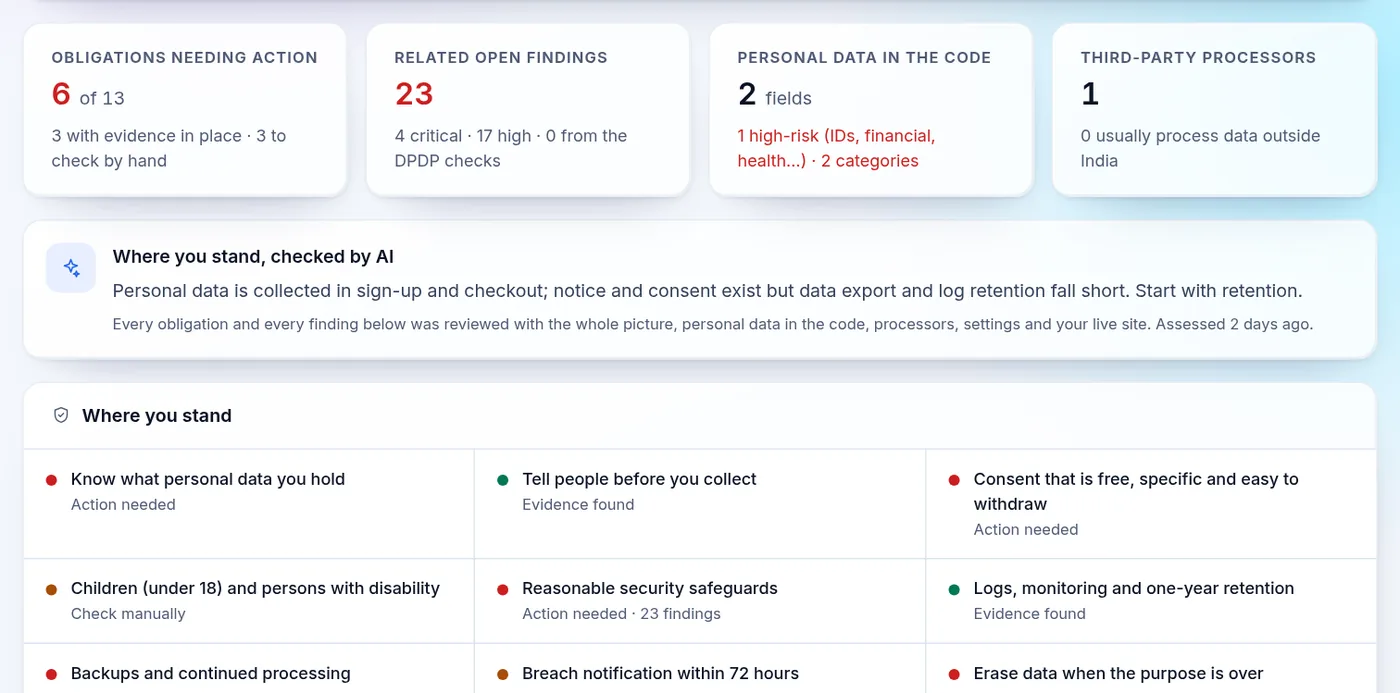
Three minutes on what Servertorch does.
With voiceover. How deep it can go on your sites, why a site went down, how attacks are read and blocked, what the plugin, file and code checks catch, DPDP readiness, and how to get started.
Built for the people who get the phone call.
Businesses
You run a shop, a booking site or a portal and you are not a server person. You want to know when it breaks, in plain words, and what to tell your developer.
- Works on shared hosting
- DPDP report you can act on
Agencies
You look after twenty client sites on hosting you did not choose. One console, each client kept separate, reports with your logo on them.
- Per-client access and reports
- A DPDP service you can sell
Developers
You ship the code and own the incidents. Guards for your framework, an API, webhooks, and a code audit that does not drown you in false positives.
- Node.js, Python, .NET, Java, Go, Ruby, PHP, edge
- GitHub and Bitbucket, read-only
Pick a plan. Start today.
Prices are on the site, per month plus GST. There is no free trial: your account opens when you sign up and the first invoice is payable straight away. Rather see it on your own sites first? Book a demo and we set it up with you.
Choose a plan
A ready plan, or build your own with the number of sites, people and history you need.
Create your account
Name, email and company. The account opens straight away, no waiting for a call.
Pay the first invoice
A GST invoice arrives by email with a link to pay by UPI, card or netbanking.
Add your sites
Outside checks start at once. Add the guard or WordPress plugin where you want the inside view.
- GST invoice with CGST, SGST or IGST
- UPI, cards and netbanking
- Bank transfer, TDS handled
- Pay a period early if it suits your books
Is your website ready for the DPDP Act?
Which trackers load before anyone consents, whether a contact for data questions is named, whether your forms record what people agreed to. Free, no sign-up, about fifteen seconds. Findings and fixes, never a compliance verdict.
We request your home page and privacy notice the way any visitor would. We do not scan for vulnerabilities, log in, or change anything.
Questions we get on every call.
Do I need to give you SSH or root access?
No, never. Outside checks need nothing at all. The guard is one PHP file you upload, or a package you add to your app like any other dependency. The WordPress plugin installs from the admin screen. Code audit uses a read-only token you create.
Will it slow my site down?
The guard does its checks in memory during the request and sends reports in the background. If it cannot reach us it fails open, so your site carries on as normal. The outside checks are one light request every few minutes.
Does it fix problems on its own?
It blocks attacks, and if you allow it, applies narrow virtual patches for new attacks and for known-vulnerable plugins until you update them. It does not edit your files, change your code, update plugins or restore backups. It tells you exactly what to do and leaves those decisions with you.
What does the AI see, and can I turn it off?
AI features are off until an owner on your account switches them on. When on, the AI reads the attack requests, findings and public pages it is explaining. Secrets are masked before code is sent, and only changed files are re-sent. Blocking and alerting never depend on AI.
My site is on shared hosting. Will it work?
Mostly, and we will tell you exactly how much before you pay. Uptime, certificates, headers, file changes and attack blocking all work. Some hosts hide server load and parts of the traffic. On Wix or Shopify only the outside checks work.
How does pricing work?
Plans go by number of sites and how deep you need Servertorch to go. We share the price after the demo, once we both know what you need. You get a proper GST invoice and can pay by UPI, card, netbanking or bank transfer.
Who else sees my data?
Only the services we rely on, each listed on our subprocessors page with exactly what it receives: hosting, payments, IP lookups and, if you switch AI on, the AI provider. Secrets, phone numbers, email addresses and ID numbers are masked before anything is sent for AI analysis. The free check never uses AI.
More on subprocessors, security and privacy.
See it on your own sites.
Send us the list. We look at your sites before the call, so it starts with what we found rather than a pitch.
No free trial. Monthly, with a proper GST invoice. Demo replies within one working day.